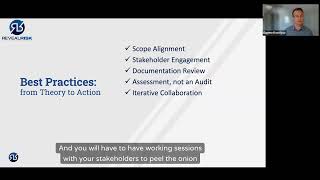
A NIST assessment isn't a pass/fail test but a collaborative process to understand your actual security controls versus what you plan to build. The team works through structured sessions to map current state, desired goals, and roadmap, using consistent scoring criteria throughout.
Chapters
And then we jump to the assessment itself. Big thing, and I'm, I'm gonna stump on this assessment. This is an assessment, this is not an audit. There is no pass or fail score. You're not doing a witch hunting exercise. You're not pointing fingers. In fact, it is an iterative collaboration between your team, your, the stakeholders that have been involved. It is truly a one team, one fight. You have to define where you are at. You have to agree on the goals where you want to be, and you will have to have working sessions with your stakeholders to peel the onion and understand how controls have been implemented, how, how they have been prescribed and what the organization is doing, because it might not be implemented, but it might be on the roadmap and you still want to account for that. As you're going, going through those working sessions, one thing to keep in mind, scoring criteria, that's a big one because it has to be uniform.