Software Vulnerability Exploitation - #cybersecurity #software #anthropic
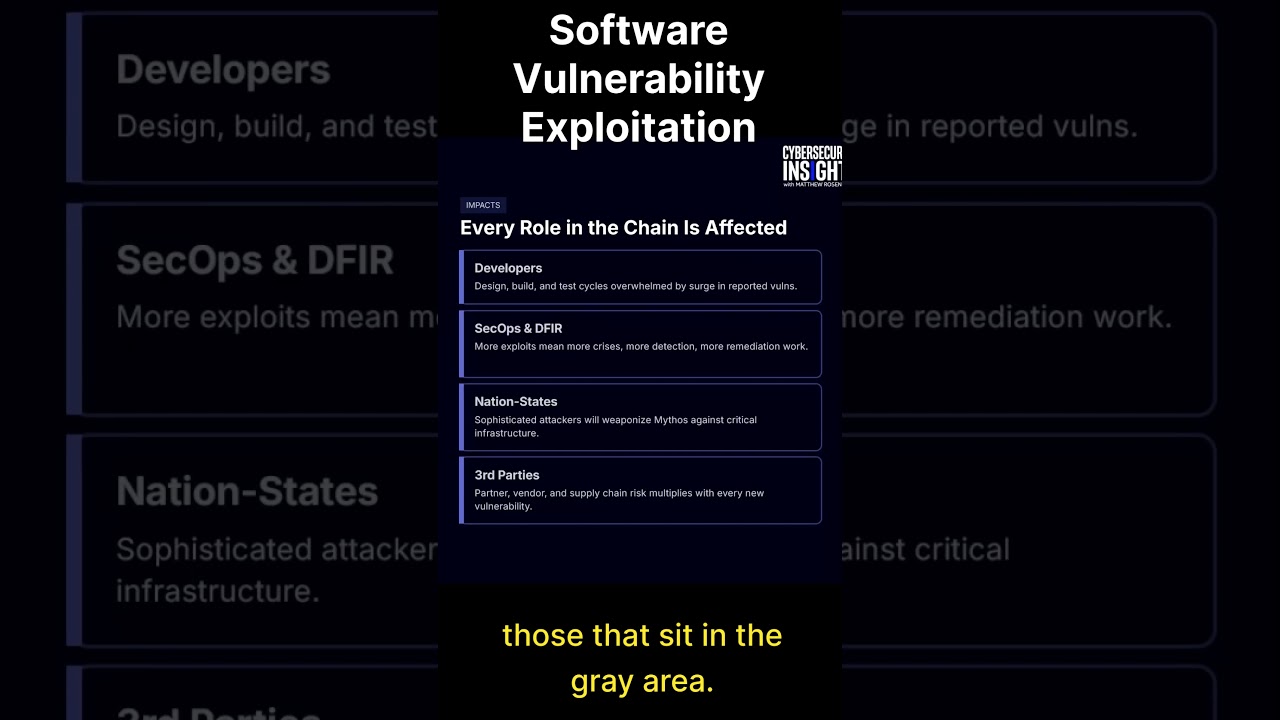
The speaker highlights a rapid contraction in the "time to exploit" – the interval between a vulnerability’s public disclosure and its active exploitation – which is moving from years to hours and is projected to shrink to minutes. This narrowing window intensifies pressure on the entire software security ecosystem. Developers must consider security earlier in design, building, and testing, while also supporting future updates. Both ethical and malicious vulnerability researchers accelerate the discovery and weaponization of flaws. Security operations teams face a surge in detection and mitigation demands. Patch developers, quality assurance, and deployment teams confront a growing backlog of reported vulnerabilities, requiring faster validation, comprehension, patch creation, testing, and rollout, all while continuing to develop new features. The overall message is that the accelerating exploitation timeline creates a systemic strain on all roles involved in securing software.
Chapters
More from Matthew




The Future of Cybersecurity: How AI Is Exploiting Technical, Behavioral, and Process Vulnerabilities






