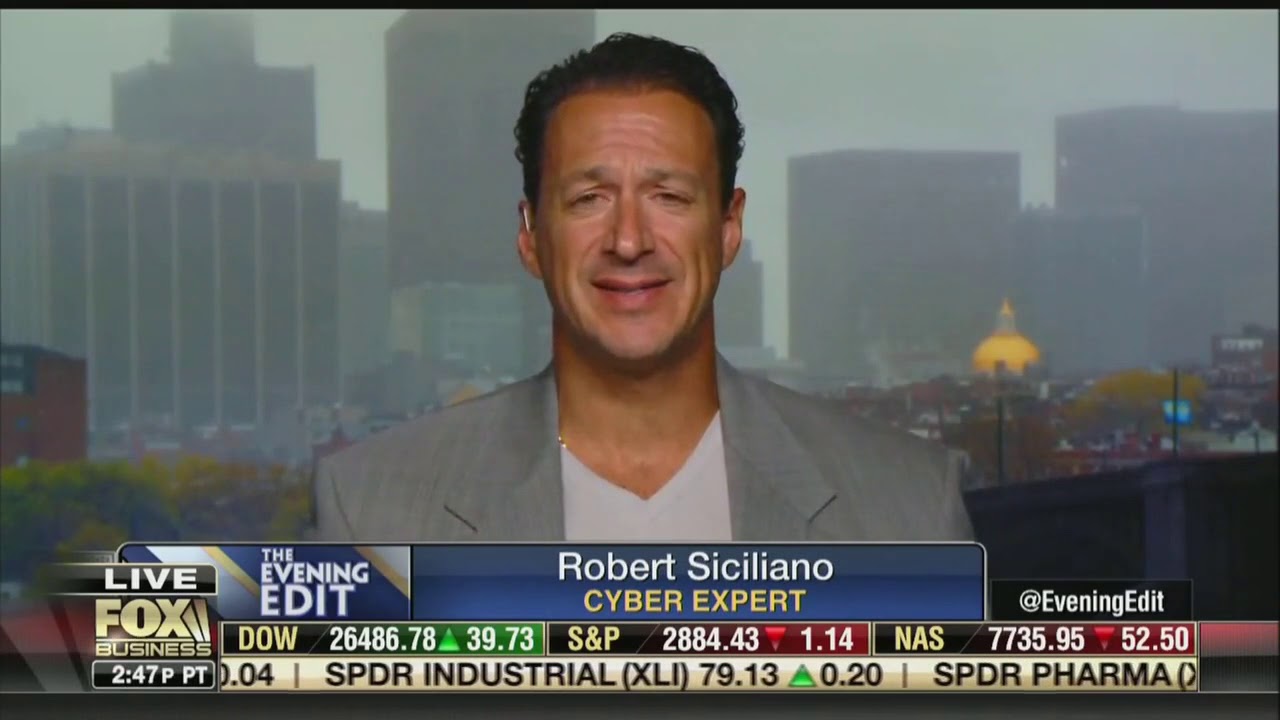
A Google+ bug exposed 500,000 users' email addresses. Cyber-security analyst Robert Siciliano says the leaked emails could be used for fraud, and that Google tried to hide the vulnerability. Both speakers expect regulatory backlash, especially from the EU under GDPR.
What a story. Hillary, thank you so much for your reporting there. Let's bring in cyber expert. He's a Hotspot Shield security analyst. He's Robert Siciliano. Pretty weak comeback from Google. Just because they didn't find any evidence doesn't mean it wasn't misused. I mean, this is weak stuff from Google's rationale here. Are they in trouble?
You know, it's just a further sign of the erosion of privacy. Certainly nobody likes the way that Google handled it. The only good news to come out of this is that the data that was essentially available was not things like Social Security numbers or credit card numbers, but it was email addresses. And in the wrong hands, that could certainly lead to fraud.
You know, Google's model is don't be evil, but then Google tried to hide this security bug. You got to imagine that the EU is going to go crazy over this.
Yeah, you know, GDPR and etc., that this is an ongoing issue that Google and Facebook and others continue to face. You know, they can only protect protect their networks to a certain degree, but then when there's operator error, when the, when the Google themselves, uh, has a vulnerability because of some flaw in their network, uh, that's a significant issue.
Yeah, I'm going to watch too if the U.S. steps in here. Thank you, Robert Siciliano. Good to see you, sir. Cyber pro there. Thank you. Even liberal HBO host Bill Maher