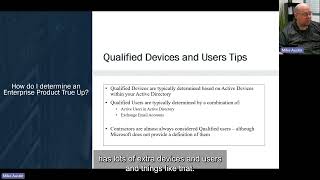
Microsoft EA True Ups - Episode 5
12 Aug 2023 · 1 min
0:55
Mike Austin walks through how Microsoft counts active devices and users in EA audits: they check Active Directory, mark anything AD-enabled as active, and use last password reset as a signal. He warns that Active Directories are often full of stale objects and recommends negotiating your contract if you want a different counting method.
Chapters
More from Mike
youtube.com
Microsoft Add-Ons Hidden Costs Explained | EA Renewal Risk & License Optimization Expertise Sharing
7mo ago
youtube.com
SaaS Sprawl Explained: How Decentralized Software Buying Destroys Negotiation Leverage.
7mo ago
youtube.com
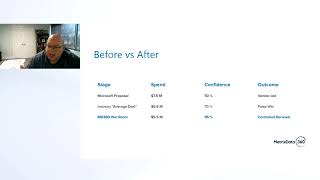
Microsoft EA Renewal Strategy: Mike Austin Explains How the War Room Method Works.
7mo ago
See all content