Mike Austin says organizations should map out exactly what Microsoft products they're using and what they're paying for before buying more licenses. He recommends running surveys, inventorying security tools, and tracking contract dates to avoid paying twice for the same protection.
Chapters
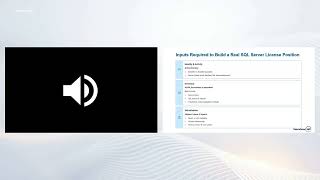
And so one of the things when it comes to data that I tell people all the time, and this is one of the key things about even when you're looking at, you know, the security piece that we're going to talk about is you really have to understand what you're using. So a lot of times I'm going to talk about the strategy that Microsoft uses when it comes to negotiating. But most organizations go out and they just sort of buy more of what they had or increase. So like if I'm on Office 365 E3, I'm talking about moving to E5 and they sort of have an idea of their roadmap, but they really don't. And so one of the first pieces of information that we talk about is actually going out and understanding your Microsoft roadmap. And when we work with clients, we have over 15 actual surveys that we do with our clients to understand that roadmap. And you can kind of see a couple of them here on the screen. But you know, like, if you look at like the Microsoft Security product, what are, what are we looking at? What do we currently have in our environment? What third parties do we have? When do those expire? What's our value that we're paying for those on an annual basis so that we can look at. If we were to buy the Microsoft Security products, is there even value in it or we just going to be double paying? Doesn't matter if Microsoft discounts the cost completely out if we've still got third party costs that we can't get rid of. And so you want to pull all that together to get a view of where you're at.