Biggest Security Risks of 2021 for Law Firms
Tom Lambotte explains why small law firms are targeted by hackers and walks through an eight-layer security roadmap. Most solo practices rely on hope that they're too small to matter. The three biggest threats in 2021 are phishing, employee risk, and COVID scams.
Chapters
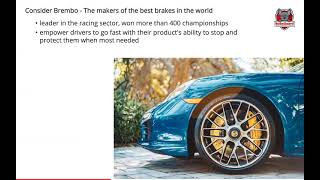
Thank you very much. Thank you for having me. I'm excited, uh, for this presentation. Um, so welcome everyone. You're here for the security class. If you're expecting something else, sorry, uh, that's what we're doing today. Um, so what we're going to talk about is how to protect your law firm from the biggest security threats of 2021 without having to become a security expert or waste a whole bunch of your valuable time. And so I'm your teacher, Tom Lambot. As Catherine said, I'm the CEO of Global Mac IT. And Boba Gard. And in this class, you're gonna discover how to protect your firm. And if you've ever depended on the most common security strategy used by solos, which is what I call the hope strategy, where you hope you'll never get hacked, you hope you're doing enough, you hope that turning on 2FA on one of your accounts is good enough, and you're hoping you're not gonna, you know, experience a data breach, I'm really proud of you for investing the time to find some different strategies and kind of, you know, get up to date on, you know, what's out there, how can I really secure protect my law practice. So first of all, who am I and why should you care? So BobaGuard is a company that I founded last year, and it's a turnkey cybersecurity solution that I built from the ground up to protect solo, small, and now we're expanding to mid-sized law firms from getting hacked. And I'm also the CEO and founder of GlobeMac IT, a company I started 16 years ago. And so we're a managed service provider, so we do outsourced IT for for law firms that use Macs. So it's a very, very specific niche, and I've written a few different books on the topic. I also like to take photo ops with famous people to make me seem more important than I really am. There's a few of the Sharks and Marcus Lemonis, and, you know, a fancy, hey, I'm on stage, look at me. So I also write a lot of content. I enjoy writing. I'm kind of a simplifier when it comes to complex technology things. That's what I've always loved. And so I have a blog series called Stupid Simple Mac Tips. I also have one called Stupid Simple Security Tips where we just kind of write— yeah, I usually shoot for 300 to 400 words, so it's really short and digestible and applicable, uh, kind of, you know, content written specifically for solo and small firms. Um, all that stuff aside, what I love the most, uh, is my family, my kiddos. I've got 4 beautiful, healthy, and happy kids, and we recently adopted a French bulldog named Boba, which you can see in the top right there. His ears are as big as his head. And we're actually going to be adopting— getting another dog on Friday, which is— they have the same dad. Yeah, one dog wasn't enough, so we're getting two. So cybersecurity threats need to be addressed, right? However, as a solo and small practice, a small law firm, you face a few different problems. First, most people lack certainty in going about it, right? Where do you start? What do you need to do? I find a lot of people have a nagging suspicion that the basic measures they're currently taking are not enough. You know, most common, they just don't have the time. And it's also really common that if you have reached out to an IT provider to get help, you were turned away for being too small. I actually had a call yesterday with a lawyer down in New Orleans who I met with 2 years ago, and at that time I had turned him away because he was too small for my managed service provider company. We have a 10-user minimum. A lot of IT companies have a, you know, 15, 20, 25 user minimum. And so over the years, I met with hundreds of solo and small firm lawyers that I knew they were too small for our service going in, but I always strive to provide value, you know, at a minimum, give them some, um, give them some direction and guidance and recommendations for what they could do. But ultimately, I knew that I was kind of turning them around and sending them back out into the world where they didn't have the resources and solutions that they were going to need. And so one of the concepts that I created is that it's kind of simplicity, complexity, and then simplicity. It's kind of an ongoing cycle. And so the legal profession as a whole, I've been in this market for 16 years now, and they've made significant advancements in their use of technology, right? Especially with the cloud being adopted really over the past 10 years, but really in the past 5 years is when it has been kind of widely accepted. And so it has brought a significant amount of simplifying when it comes to the technology, right? So you look at Clio and Rocket Matter, the first case management solutions that were SaaS applications came out in 2007. And today, a lawyer can get almost everything they need set up really quickly, right? If you need to, when you're opening up your new practice, you can set up 365, your email, contacts, calendars, file sharing set up on Box, and integrate these services with your favorite case management solution all in one afternoon, right? So as a result, a full 40% of lawyers has said that they're likely to turn to internal tech support for problems with their firm's technology. So that's another way of saying, hey, when I have a tech problem, I go to Google, I figure it out myself. And what I found is when you've got, you know, usually 2, 3, 4, 5, 6, 7, I think, I, Usually when you get to 8 people or more, that's when it starts getting much more complex, and that's when it usually makes sense to get an IT provider. But even then, not all the time. You know, we just signed a client with 10 users last week, and he's like, hey, I got a pretty good handle on the technology. I'm comfortable managing the email accounts and all that stuff. Where I'm not confident is the security part. And so there's been, again, a lot of progress, a lot of simplifying, and that's a direct result of the progress made through adopting all these new technologies that have empowered solo and small firms to practice at a much lower price point, right? 10 years ago, you had to have an exchange server hosted, you know, on in-house somewhere. You'd have to hire an IT person to get it all configured, and it cost big money to get set up. Now, as the great philosopher of the '80s band Poison, Bret Michaels, sings, every rose has its thorn. So on the flip side of that simplicity is, is that Alongside it, there's a new complexity that was introduced. And so as the technology became easier to use, cyber criminals have and continue to become more and more sophisticated, right? So this image here is a list of many of the solutions that exist to protect businesses from cybersecurity threats. Um, you're probably confused or overwhelmed. I am too. And I look at that thing, it's like, oh my gosh, it's just me, right? It's just me and a paralegal. I don't, I don't have that much complexity. And so Most people, you know, most of you do not have an IT company proactively providing advice and guidance on all the latest security threats. And since the role of security falls under managing the technology, what's happening is that the majority of solo and small firm lawyers are grossly underprotected, and they don't even realize it. And the problem is that 49% of private practitioners in the U.S., about 760,000, 49% are solos. And another 14% are in firms with 2 to 5 lawyers. So that makes up 75% of all lawyers are in firms with 5 lawyers or less, right? And so the majority of them, they want to do the right thing. They want to make sure that their content is secure, their, their data, their client files and all that stuff, but they don't know where to start. They don't know where to go. Now, the Romanian sculptor Constantin Brânskuși said that simplicity is complexity resolved. And so that is why we are here today. So today's webinar is for you if you want to discover the biggest cybersecurity threats to watch out for this year, if you want to find out why 29% of solos and small law firms have suffered a data breach and how you can protect yourself, and if you want to tap into expert knowledge to quickly advance the security measures of your law firm. So if that's what you're looking for, this is for you. Now here's, you know, here's the truth: you will never be able to secure your practice from cyber threats and the risk of a data breach 100%. If any security solution provider claims to provide 100% protection, run the other way, because that's impossible, just like a car having a 100% safety rating. So that being said, what you can do is take reasonable efforts to drastically reduce your risk using affordable solutions. And so that's the kind of trifecta, right? When you can get all those three together, you can make massive progress in your security. However, I have admit that I didn't always take security seriously enough myself. In, um, so since 2006, I've been running Global Mac IT, right? We're a managed service provider for law firms that use Macs. And in 2012, I experienced a frighteningly close call when our biggest client at the time, a leading South Texas law firm with a strong reputation as civil litigators, came super close to becoming a victim of a data breach on our watch. And so this really shook me to the core because I realized how close they had been to facing hundreds of thousands of dollars, you know, in damages and corresponding fines and lost revenues and all that stuff. And so I had told myself up until then that, yeah, security is one of our top priorities, but going through this made me really face some hard truths, you know, and the truth is that our clients were at risk and we had to do more. Now, one of the problems that I had is we just worked with Macs, and Macs have always been more secure than PCs, and I'm not here saying that's not true anymore, right? But I also became keenly aware that a lot of Mac-using lawyers were actually very lackadaisical towards security because they were using Macs, right? So the mindset was, oh, we use Macs, so we don't need to worry about security, right? And that was true 10, 15 years ago to a certain degree, but today the landscape landscape has really evolved, the threat landscape. So, you know, back then I took pride in the fact that we didn't even run malware or antivirus software and that I had never had one Mac on my watch, you know, been infected. So I myself was perpetuating the behavior of inaction. Okay, however, facing that, you know, that close call led me to a lot of sleepless nights, a lot of stress. It was not fun, and as a result, we drastically changed our entire approach to security. Right? Again, we were not doing enough to properly address the evolving world of cybercrime. And so I made a commitment at that point to not only include all the security layers needed, but to seek the absolute best in class. And so as a result, we ended up spending thousands of hours researching, testing, and rolling out, you know, the best in class security solutions, really finding like, hey, what actually helps? What moves the needle? What actually gets results and increases the security? And so we tested dozens of security solutions internally. My system admin spent thousands of hours doing this over the years. And now we depend on all of these solutions to protect our company and all of our clients. And so whenever we sign up a client under GlobeMac IT, implementing these solutions is not an option. So it's like, hey, this is what we do. So as a result, you know, our clients have been able to go, you know, through a transformation from a state of uncertainty in regards to their cybersecurity risk and protection measures to a state of certainty. And so in order for lawyers to build your law firms, you've got to have confidence in your security measures, right? You've got to know that you're covered if something happens. That's why we cover— you know, that's how we have liability insurance and car insurance and all these other things to protect you if and when something happens. Now, my why, like the thing that really drives everything that I do and, and the reason I created BobaGuard and why I'm, you know, doing these presentations and so forth, is because my— I am passionate about helping entrepreneurially minded lawyers grow. And that's my biggest passion that drives me daily. And I love to help others. And, you know, solo lawyers and small firm lawyers are the most entrepreneurial, you know, lawyers out of all of them. Right? If you're working for big law, you don't need to be entrepreneurial. You can just practice law and just focus purely on that. So Boboguard was built specifically to provide the answer to these problems. Okay, the idea was to simplify the complexity that's inherent in getting the right security measures in place. Now, how does my passion to help entrepreneurs grow tie into a cybersecurity solution, you might be wondering? So an analogy that I have is Brembo. They are the makers of the best brakes in the world. Right, so on the surface, uh, they are brakes, they help the car stop. But in reality, being a leader in the racing sector who's won more than 400 championships, what the Brembo brakes really allow the drivers to do is go fast with their product's ability to stop and protect them when most needed, right? They're able to, you know, gun it into the turn because they know that their brakes are going to do what it needs to, you know, when it comes up. And so I believe that protecting solo and small firm lawyers like you empowers you to go fast, focus on growth and focus on building your practice. So when I went through, you know, kind of that big scare in 2012 and all the action that came afterwards, there were 3 key lessons that I learned that I want to share with you. And so the first lesson is that the likelihood of a data breach is far higher than you think. And the 2020 ABA Tech Report, you know, states that the number of firms experiencing a security breach increased over the prior year 29% compared to 26% in 2019, and it was 23% in 2018. So the, the path is not going in the right direction. The second lesson was that most solutions out there are not created or built with you in mind, the solo or small firm lawyer. Okay, um, you know, the majority of, you know, what gets attention, hits, and results are the big companies selling big products to big enterprises, right? If I'm building a cybersecurity solution, if I can sell it to one of the big law firms and has, you know, 500 or 2,000 people, I'm going to make a heck of a lot more money than selling it to 2, 3 solos, right? And so the, the problem, again, most IT companies, what they do, um, is they have that 10— they might have a security stack, but they still have the 10, 15, 25 user minimums, or they want to do all the IT for your law firm and do the security stack. No one has gone out there to kind of simplify it, you for the solo or small firm lawyer and it kind of made it accessible. And again, I've turned away hundreds of lawyers, you know, over the past 16 years, and that's really why I went out to, to build this, because I started feeling really bad and I was like, man, I know they don't have— they're not— they're, they're going to go back out there when I turn them away and they're not going to be able to find the solutions they desperately need. And so I started asking myself, how can I help them? How can I bring value? How can I create a solution? Because the biggest issue was labor and resources. So the third lesson is that most lawyers lack the time and skills to adequately protect themselves, right? So you've got a lot of roles that you need to fill, and when you have so many different roles that you're responsible for, what ends up happening is that the squeaky wheel gets the grease, right? So the problem is, in this case, what we're talking about is that a squeaky wheel is, is equivalent to data breach, and that's too late, right? We've got to stop it before that happens. Near the end, I promise to share with you how to implement this knowledge in your practice without further demands on your time. What we're going to focus on today is a framework that I've created called the Lacking Framework. If I can copy it, I've got a link where you can grab the workbook that goes along with this. Give me a second as I struggle with technology. I always like to share that I struggle with technology because I think it makes other people feel better when they see the IT guy struggle with technology. All right, let me see if I can share this link here. So someone could try to click on it, uh, go put a comment, uh, in the note, um, you know, yes, the link works. I, in the past, sometimes I've had it not work, so let me know. So when, when you're protecting your law firm from cyber threats, there's 4 key things that are lacking that must be addressed exist and that can keep you at risk— uh, thank you, Brooks— um, that keep you at risk of getting hacked and that are the primary causes that 29% of lawyers have been breached. And so I call it the 4 L's to a secure practice. So the first lack is a lack of awareness. What that means to me is not knowing what the threats are. And this shows up in a few different ways. You know, first, again, is the most popular strategy, the hope strategy, also known as the ostrich strategy. You know, it's not it's not going to happen to me because I'm just a solo. It's not going to happen to me because I just do family law and the criminals are after the IP lawyers, right? Um, so by falsely assuming that they're not going to be targeted, most solo and small law firms do not properly protect themselves, right? Back in the '80s, seat belts were optional, right? It's like, I don't need to wear my seat belt. Now it's a no-brainer. Everyone wears their seat belts, right? Um, so again, believing that the basics are enough The fact is they're not, and we're going to talk about that a little bit more. And also just not being up to date on today's biggest threats. Now here's the kicker. Again, the lack of protection gives cyber criminals a huge advantage and easier access. In other words, cyber criminals know this and they're capitalizing on that fact. They know that the majority of you still think that you're too small to be targeted, and, and so you're very lackadaisical on your security measures that you're taking. I want to share a story here, and this was, uh, it's about a lesson that was learned too late by this hard-working solo attorney. Shannon was a solo family lawyer in California, beloved by friends for an approach so tenacious they called her El Toro. And like a real bull, she charged aggressively forward while forgetting to guard her flank. And believing that her practice was too small to be targeted, she hardly bothered with online security practices until her case management management system was breached, and as a result, she had to notify the authorities, her clients, and all related parties that their data had been compromised, right? And so this is a, you know, this is a picture here of the notice of a data breach she had to file with the DA. Um, and I didn't know her personally, but actually did a search on the dark web under her domain, and I found one hit, a single set of password credentials, and the password was her first name. So I don't have 100% confidence that that is what led to the breach, but it's very likely and quite possible. The dates of when that credential actually went on the dark web was within weeks of May 5th, 2018, from when she actually was breached. So had she understood the risks, she would have taken better precautions, right, using a password manager, unique passwords, credential monitoring, system alerts, and she could have easily avoided the nightmare that damaged her reputation, her firm, and years of hard work. Work, right? She has now slowly and painfully rebuilt trust in the business, but you should— I see so many examples and events like this happening, and I don't want you to learn the hard way that she, you know, the way she did. As you can see here, 57% of small businesses do not think a data breach will happen to them. However, 29% have experienced a data breach, so you've got to ensure everything you work so hard to build is protected. The next part under, you know, lack of awareness is believing that the basics are enough. Maybe you feel safe because you practice minimal cyber hygiene, right? Maybe your favorite password, you keep it in a drawer instead of, you know, stuck to your monitor. Maybe you have two-factor authentication enabled on two accounts, right? Admittedly, these measures alone are far better than nothing, but barely. So again, in short, basic protection is not enough. If you experience a data breach, do you think your ethics board is going to give you a gold star for doing the absolute bare minimum? Um, I don't think so. Um, so the next one here, uh, Thomson Reuters has a great report, the State of the U.S. Small Law Firms, that comes out every year, and they state that 60% of small law firms want to upgrade their IT security, but less than half currently employ basic security measures. So it's like, yes, I want to do this, I want to lose 30 pounds, but I'm not willing to eat healthy or exercise. Right? And the last one with, with the lack of awareness is not staying up to date on today's biggest threats. You know, this image here has a handful of, of current security threats that are out there. I'd love to address them all, but that's unrealistic. So I'm going to talk about the top 3 that I believe are the biggest threats to solos and small firms right now. The number 1, the first here is phishing and business email compromise. So these can show up as spoofed emails and websites based on legitimate contacts, and what they do is they extract credentials granting access to sensitive information, finances, or systems. So I'm going to share a real-world example of this in just a few minutes. The second biggest cyber threat are employees, and even well-intentioned employees pose threats by succumbing, by falling to phishing schemes, by reusing passwords, by accessing systems on unsecured networks, or or accidentally deleting files. And then you've got disgruntled workers that can, you know, further abuse access to wreak havoc on unsecured setups. Now, if you have 1 or 2 employees, what I have found is the smaller you are, the more likely it is that you think everything's always gonna be perfect with your employees. I had this belief, you know, 10 years ago, and then, you know, at some point you have a Dr. Jekyll and Mr. Hyde moment with one of your staff and you lose a whole lot of sleep and you're trying to lock everything down. And it's not good to be in a reactive state, right? And so the third threat is, you know, right now COVID-19 scams and cyberattacks. Criminals know how and when to prey on fear and uncertainty. And so there's been a 46.9% decrease in email threats from quarter 2 to quarter 3. Over a million hits on malicious URLs related to COVID-19. And so the exploitation of the pandemic has been rampant, with malicious entities hovering around vaccine databases, you know, the PPP loan programs. I'm sure you all heard about, you know, the fraud, all the stuff that was going on, government stimulus payouts, right? So that's the second— the first lack is lack of awareness. The second is a lack of time. Right? So it's simply a lack of time to research solutions. So let's say, okay, hey, I'm aware of the issues, I know I got to do something about this, how do I go about it? And so overwhelm is a real challenge that most of you face daily, rarely share publicly, and, and let alone, you know, admit to yourselves. And when I started, you know, in 2006 working as an Apple consultant, uh, billing hourly, I would bill my butt off in the day, right? Stack as many billable hours as I could, and then I'd work 2 to 3 hours at night replying to dealing with admin, HR, finance, technology, marketing. Can you relate? So the reality is that a lot of you do not have the time to execute all of your responsibilities at a high level. Again, a solo and small firm runs, you know, leads a completely different life than a lawyer, you know, at one of the big law firms. There's so many different responsibilities and things you've got to stay on top of in addition to practicing law. And so in your effort to attend to all of your responsibilities, many areas end up getting shortchanged. At least, you know, for a while, then you kind of catch up. And so getting behind in your books for a few months is okay, right? Then you can power through it in one weekend and get caught up. However, experiencing a data breach is not okay, right? That causes very real significant pain and heartache. One of my favorite books from last year is called Who Not How by Dan Sullivan and Dr. Benjamin Hardy. And something he said in here is that time is finite. We all have 24 hours. Before you can master any of the other freedoms, you must become a master of your own time. You can accomplish a million times more if you stop asking how and start getting who's. And so the idea behind the book Who Not How is that most entrepreneurs, when they have an idea or something they want to achieve, the first question they ask is, okay, great, how do I get this done, right? How do I do this? But the problem is it ends up tying your time, right? It's committing more of your time to do it. So let's say— I know a lot of lawyers who are like, hey, I'm not going to hire a web guy. I'm gonna— I've heard WordPress is super easy. I'm going to spin up WordPress and use a template and make my own website. 80 hours later, you know, they find out that they could have hired a friend to build their whole website for $1,100, and they're like, oh man. Um, I'm guilty of this. I did this many years ago as well. So again, time being a finite commodity, small firm lawyers should find efficient solutions to internal operations and management to optimize the amount of time they can spend practicing law, right? What actually leads to billable hours? What leads to generating revenue? Anything that does not, see if you can outsource, you know, automate or hand off to someone else so you can focus on what you do best. Now, it might be true that small firms don't have much time to devote to cybersecurity, but even truer that they're running out of time to address it. A lesson one lawyer almost learned too late.
Late.
Jason was a young lawyer, tech savvy enough to realize that he needed better cybersecurity protections in place, but too busy building his practice to make the time to address it. And so he had actually rescheduled 3 times with me over a couple months to sit and discuss our security solution. Out of the blue, I get an email from him on October 7th last year, and it said, hey Tom, our opposing counsel's email was hacked. The perpetrator had emailed Jason asking him to open a file, and the perpetrator was an opposing counsel he was working with on an active case. So it was, you know, it was time sensitive, it wasn't unexpected, right? And so the perpetrator emailed and said, "Hey, I just sent a document for you now. Please check your inbox or junk folder and refer to the documentation as it's very important." To be safe, Jason replied and requested the file be sent directly. Immediately. Here's where it got crazier. Just a few minutes later, Jason got a reply from the perpetrator posing as his opposing counsel. Thanks for your kind response. The requested email is legitimate and has been secured to your email. Kindly proceed to the document with your email to gain access and let me know your thoughts immediately. This is eerily advanced, right? And this kind of, you know, situation is actually extremely common. It's called business email compromise. It's very common Now, when cyber criminals get access to someone's email account, they don't go in and spam, you know, send Viagra offers to everyone in the, in the contact list. Instead, they lurk in the shadows. They read your inbox, they read your most recent sent folders, recent messages. They know what keywords get the juiciest info, so they might type in routing number, password, Social Security number, wire transfer, right? Everything is perfectly indexed and right at their fingertips. And then what they do is they wait for the opportunistic time to intercept, right, and kind of send something out. And this story for Jason immediately shifted his reality. You know, his opposing counsel was a small 2-attorney firm, just like Jason's, and Jason decided then and there that he never ever wanted to go through that experience. So it might be true that small firms don't have much extra time to devote to cybersecurity, But you don't want to keep putting it off and putting it off and putting it off until something happens. The third lack is a lack of clarity, right? So you know that it needs to be done, you're aware of it, you know, you know, the challenge of time. And the third thing is, you know, if you want to make progress, where do you start, right? What are the solutions that exist out there? So how do you mitigate your risk? What solutions exist to protect to you. And again, that introduces a new problem. How do you find the right solutions for your needs? This image here is just a few cybersecurity solutions, right? The market is absolutely flooded, and the current market value is $120 billion, and it's going to go up to $300 billion by 2024. So it's easy to understand why so many solutions exist. The problem is, how do you figure out which ones are right for your needs, right? What do you need? How much is too much? How much is too little? What's adequate coverage to meet your needs without busting your budget. And so if you go out and just do general, you know, web searches on Google, it's typically going to leave you with more questions than you started with, right? You're going to find hundreds of solutions, and the ones that are most heavily branded that come to the top of the search results are often the larger ones for enterprises with 1,000+ employees, right? So a solo does not need a SOC, which is a security operations center. It's totally overkill. Kill, right? You don't need penetration testing on a regular basis. The solutions that are being sold to big law are not the right solutions for you. And until you have confidence in the solutions that you select, you're not going to be able to move forward, right? That's a really good reason to procrastinate. I, I don't know what to do. Until you're confident, you're not going to be able to take action. Some of the solutions out there that exist are, you know, two-factor authentication, password managers, VPNs, full disk encryption, dark web monitoring, cybersecurity training, simulated phishing campaigns and reporting, cyber insurance policies, security policies, email backup. Which one is the best one, right? The answer is, you know, none and also all of them, right? There's not just one that, that's the best. Oh, if I were to get just one, which one should it be? You know, the, the best way to have an effective security practice, uh, you know, in place is similar similar to the classic heist movies, right, where a team of burglars must get past obstacle after obstacle, each one providing its own challenge, right, before finally managing to gain access to the valuable jewels or make off, you know, with them into the night. So the first security layer might be the locked doors and windows. The second is an intrusion detection system, you know, alarms. Then you've got armed guards. My favorite one is always, you know, the laser beams. Right, that they blow smoke and like jump and do all that stuff. And so they have to get through all the different security layers to get to the prize. So it's the exact same, you know, kind of parallel analogy. The more security layers you have, the better you are. You know, you look at a car, it's the exact same thing. You don't just get a car with seat belts. You have seat belts, anti-lock brakes, airbags, you know, lane detection warning systems, right? And, and newer solutions are coming to continually make it, you know, safer. For this illustration here, I'm going to steal a scene from the classic film Almost Famous. If you want to put in the chat if you know and love the movie, just say, I know it and love it, because I think that's really cool, because not enough people do. It's a great James Cameron flick. This example is more poetic and less depressing than a real example, and I just really like that movie. Here in the scene is about to hit it big, but they resist hiring a professional road manager, believing that it's all about the magic of music and that they've gotten along just fine without one. The manager, which is actually a cameo by Jimmy Fallon, salutes their artistry but exposes their cluelessness with a series of questions outlining unanticipated issues and higher-level logistics. And so he wraps up by saying, "I didn't invent the rainy day. I just own the best umbrella." umbrella. Heck yeah, Hannah, awesome. It's a clever way of showing that the group doesn't even know what they don't know about looming problems, and frankly, they don't need to. They should focus on playing tunes and let professionals take care of the rest, just as you should concentrate on practicing, on growing your firm, while letting legal technology, you know, consulting services provide and take care of your security umbrella. The fourth and final lack is a lack of implementation, not having the knowledge or the time to implement the solution. Going back to who, not how again, when you have a new project, an entrepreneur instantly will ask, how do I do this? Instead, they should be asking, who can we get to do this for us? And taking it a step further, who's the best one for your needs? And if you think that way, all kinds of interesting ideas and collaborations become feasible. To really succeed and reach a higher level of performance, you have to shift from a how mentality, which ties you down to doing everything yourself, yourself to a who mentality, which frees you and frees up your time. And so by focusing on who you work with rather than trying to do everything yourself, you're going to find levels of achievement and productivity that rise at the same time as you also get more freedom. So you've got to focus on being the who for your clients. What do you do best? And, and expand the time you spend doing that. Let's see how this plays out in the legal This is, again, this is from the Thomson Reuters 2020 State of the U.S. Small Law Firms survey. And the key metric I want you to focus on is the guide at the bottom, right? So the blue says, we have implemented changes to address the issues. So in my mind, that's like a pass. Yes, you knew the problem and you did something to fix it. The gray, we have a plan to address these issues but have not yet implemented them. Intended. It's like, yeah, I know I gotta lose weight, but I haven't, you know, done anything to, to move that forward. And then the oranges, we haven't yet determined how to address these issues, right? I know I got a problem and I have no clue how to fix it. So the survey here for these two examples— and, and the, the report actually has a good dozen different scenarios and that are very similar— is they show that 89% of solos and 78% of small firms with 2 to 6 lawyers either don't know what to do or have a plan but have done nothing about it when it comes to spending too much time on admin tasks. When you look at increasing complexity of technology, only 29% of lawyers have implemented changes to address the issues. And if you lack the time and the expertise to secure your practice, and the industry as a whole has a hard time with addressing challenges what are the odds you're going to wake up one day with all the skills to adequately protect your law firm from getting hacked, right? So the sooner that you accept that, the sooner you can start making progress and finally get the security measures in place, you know, that you need so you can sleep soundly. David Eltringham is a client for many years now, a good friend, and in November 2018, he learned that someone had attempted to fraudulently wire funds from a law firm-controlled bank account. Okay, and so this is in his own words here: We were with a different IT provider, an hourly pay-as-you-go type, and got badly hacked. The funds in our trust account were almost transferred to Hong Kong. That was the aha moment. What we had been doing was not working, and we needed to do something entirely different. You can't imagine the carnage that that does to a small business, having to send out that kind of letter. As a result, the phone stopped ringing. They had— they were a small firm. I think they're a total of 8 people, maybe 2 or 3 lawyers. Um, and I mean, he told me, he's like, Tom, we lost hundreds and hundreds of thousands of dollars. You know, he's like, the impact is the cost of sending out the letter and the monitoring and all that stuff was the smallest expense. The biggest loss was, again, the phone stopped ringing. Um, and so he continues here, but what was really freaky for me is that when I got the list of stuff we didn't have and that had never heard of that we should have been doing. Our liability would have been off the charts for negligence. It would have been potentially gross negligence because of the exhaustive list of stuff we didn't have to adequately and reasonably protect ourselves. At the end of the day, you don't know what you don't know. And for a law firm to say, well, gee, we had no idea— I mean, how does that play in court? So I think the thing with BobaGard, I sleep well at night and don't worry about the things that used to keep me up. So one final quote from Who Not How: when you're trying to accomplish something challenging or difficult that you've never done before, you probably need a who. Let me say that another way: you absolutely need a who if you're trying to accomplish something new and challenging, unless you're fine not getting the result you want in the near future, right? Whenever you learn something brand new, it takes time. You've got to figure it out. Yeah, you know, it takes far longer than it should. When you get the who, that's like, hey, this is how we do it. And again, that's what a lot of you do for your clients. So now that you understand what holds lawyers back from securing their practices, you might be wondering, what solutions can I leverage to protect my practice? So I'm going to share 8 different security layers that, that exist, uh, that are really good, you know, in my mind, some of the best methods to protect your law firm. So the first one is security— is, uh, fund cybersecurity training that doesn't suck and can't be bypassed. Can't be bypassed. What I mean by doesn't suck and can't be bypassed, if any of you have ever gone through a cybersecurity training program, I have never met someone that told me it was awesome, I learned so much, it was so engaging, right? I don't think anyone has ever described a cybersecurity training program using those words. It's usually the bipolar opposite. It's dull, it's monotonous, it's way longer than it should be. As a result, what most people do going through the cybersecurity training is they, they tap out mentally, right? You might even mute the video, wait until it ends, and then what I wrote with can't be bypassed, then the question pops up to see if you were paying attention. And I call these stupid simple questions, meaning you could ignore the entire video and pretty much guess what the right answer is 9 out of 10 times. So as a result, you know, you might be going through a cybersecurity training, but you and/or your team members are not actually learning, you're not benefiting. And so The, the better cybersecurity solutions nowadays, you know, can be fun and easy. They use behavioral science techniques like storytelling. You know, they've got to be short, you know, 5-10 minute videos so they're engaging, you don't kind of burn out. And then the questions should be tied to the actual content in the videos, and so they can't be, you know, they can't be ignored, you know. So as a result, you end up learning a lot more. So cybersecurity training is one of the best ways to protect yourselves. I also want to warn you you just because you're the owner of the practice. And typically the owners have obviously more skin in the game. And what I found recently is you might think you'd never fall for a phishing email, but it's happening very often on a regular basis. Neil Tyra is the host of a great podcast for solos. It's called The Law Entrepreneur. Entrepreneur. And, uh, but we did an interview a month or two ago, and the same day, that afternoon, he fell for a phishing email. And he is tech savvy, you know. He told me, he's like, yeah, you can tell people my story, you know. But he got an email from a friend of his, another lawyer. Email signature was exactly the same. Clicked on a link, uh, took him to, you know, kind of a website with a login page. The website was a mirror copy of his friend's home page and website, down to the— what's the word— a fluid, you know, kind of modern design. So I mean, it was an extremely convincing website, and he put in his credentials and he fell for it. And right after, he's like, oh my God, and he called his friend, and sure enough, he fell for a phishing scheme. So it can happen to everyone. So everyone needs to go through the cybersecurity training, even if you think it would never happen to you. The second security layer you've got to get into place are IT security policies. And this provides guidelines to employees on what to do and what not to do. You've probably heard before that the cobbler's son has no shoes, and this is definitely true when it comes to lawyers. So, you know, we're talking about an acceptable use policy, disaster— business disaster recovery policy, things of that nature that you've got to get into place to protect, you know, protect yourself and your team. And so this helps you establish expectations and explaining repercussions to protect your business, and it helps you meet requirements if you've got to comply with PCI PCI, HIPAA, GDPR, FINRA, and so forth. The third security layer is dark web monitoring. And so 61% of breaches involved credential data. So the majority of people reuse passwords, right? I believe strongly that most people have 3 passwords. They've got the password they always used. At one point, they're, you know, the website logged into said, hey, that one's not secure enough, you need a number. So you took the same password and you added a number at the end, and then your bank at one point said, hey, that's not secure enough. So you kept the same password with the number and you put an exclamation mark at the end. Maybe you even went super, you know, tricky and you made the S into a 5, and you're like, haha, no one's ever going to figure that out. So that is extremely predictable. And the problem is when all these third-party data websites get hacked, right? When you hear about Chase and Target and Netflix and, you know, Facebook, LinkedIn, Yahoo with 1 billion username and passwords, right? The criminals don't get paid when they actually steal the data. The criminals get paid when they go to the Amazon for criminals, which is the dark web, and they list them on the dark web and they say, hey, I've got, you know, 20 million credentials here with passwords. Other criminals come in and say, hey, I'll take 2 million of those. I'll take 10 million from the Target breach. How about let's make another million from Home Depot, and then they take that data and they start testing them out. Hey, does this work on Catherine's 365 account? Does this work on Marty's Clio account? How about Ellie's, um, you know, QuickBooks? And so that's when they go shopping, and that's how they get in, access a lot of content. A few years back, uh, NIST, which is a National Institute of Safety and Transportation— they are the organization that taught everyone that said, hey, When— oh, they're the ones that taught everyone to change their passwords every 3 months, right? For years and years, for 20 years, we were all taught to do this. So every 3 months you were prompted, you put a different number at the end, and then you just recycle the same passwords. So NIST realized that, hey, that advice is actually really bad and it forces people to create, you know, really weak passwords. So they changed their recommendations, I think about 3 years ago, and they say, well, we don't recommend that anymore. What we recommend is that that you only change your password when it's been compromised. Great advice, but the next question is, okay, how do I know when it's been compromised, right? How do I know that a third-party website, which I have no control over, gets hacked and that data gets listed on the dark web and now criminals have access to it? So that's where dark web monitoring comes in. So it proactively monitors stolen and compromised data so that as soon as a hit comes, you know, with your, your, under your email domain for your practice, You get notified, you can check to see if that password's in use, and if it is, you can change the password, essentially changing the keys, you know, to your house. Um, security layer number 4, um, everyone is getting phishing emails, uh, so why not send out phishing emails to yourself and your employees as well to see who's going to fall for it, right? So that is what phishing simulation is, phishing training for employees. Um, so this helps you Again, educate your employees. You're doing the cybersecurity training, you're doing phishing simulation, and that way you can find out who's struggling, who's doing really well, right? Who's falling for it? Who clicked on the link? Who not only clicked on the link but also put in their credentials, right? And so again, this helps everyone on your team, really the frontline, from spotting and stopping, you know, phishing emails. The next security layer that we recommend are tools on your Mac or your PC that take care of proactive monitoring, maintenance, and patching, along with antivirus and web protection. And so what these kind of tools do is they automate software patches and security patches for your Apple and Windows computers. They also do preventive monitoring and alerting of IT incidents, right? So if you've got a hard drive that's starting to fail or if your battery life is quickly degrading, you know, it'll notify you make you aware of those before your computer fully dies when you're in court, you know, or something like that at the worst possible time. They also include antivirus and malware, right, scanning and removal, and DNS web protection, which blocks malicious URL domains. So what the DNS web protection does is let's say you fall for a phishing email and you click on the link, it's very likely that that link is gonna be automatically blocked. So the DNS web protection, it's like continuously updated from users around the world of malicious, right, bad URLs, and it adds them to that list. So if you click on one of those URLs, it'll give you a warning sign and kind of stop you from going to it. So again, the idea is layered security. All these different things, when you stack them together, you're going to be far less at risk of getting breached. The next security layer here is, is insurance. So it's more coverage. Again, like I said, there's no 100%, you certainty that you're never going to get hacked. So if and when it happens, cyber insurance policies, I think eventually they're going to become required. That's not the case just yet, but your business and financial security depends on how well protected you are from a lawsuit or a claim. So insurance policies will include investigation to help you figure out who or what was compromised, coverage for fines and penalties. You have to provide credit monitoring and notification and legal defense and liability expenses.
Expenses.
To give you an idea, I believe it's an average cost of— I want to say it's $151 per record in your database, right? So if you're breached, you have to file a notice of a data breach with your local district attorney's office, and you have to provide credit monitoring. You have to send out a letter to every single contact in your database. Let's say it's your email. These are your current clients, previous clients, potential clients, opposing counsel, judges, other lawyers you work with, referring attorneys, right? So again, it's a horrible, horrible scenario. So we want to do everything we can not to get to that. But if you get to it, you want to make sure you've got the insurance in place. Now, the problem with insurance policies— Catherine and I had a good talk about this actually a couple months back. Most policies are— when you try to get a cyber insurance policy, there's a very complicated application process. Catherine had— and Catherine, you can jump in and correct me if you want here— but the way she said it, I think she had had a handful of lawyers reach out to her like, Hey, can you help me fill this thing out? Because there are a lot of these questions are over your head. They're very technical and, you know, firewalls and things like that. And so she ended up creating a training specifically to help people fill out the application form. So the— yeah, it can be a little tricky to get those done. You want to add to that?
Well, it's— this is even, I guess, scarier. It wasn't a cyber liability policy. It was specifically So when I worked at the Chicago Bar Association, we had an insurance brokerage and so they would shop out insurance policies. And one of the insurance policies requested, the attorney brought me the application and she goes, I don't know how to answer these. And it was not in North Carolina, so don't panic, but it was a major national insurance company. Just malpractice insurance coverage, not the, um, not the actual cyber liability policy, wanting to know how she was backing up, whether she had a firewall, whether she had her hard drive encrypted, and all that stuff. So we just went through, and it was just a— she's a sole practitioner with one computer. So we went through and applied a bunch of the, the security to her computer so she could answer the questions in the affirmative. But, you know, when your malpractice insurance provider's starting to ask these questions, um, you would imagine that the cyber liability policies are also wanting to know because they're not in the business of insuring high-risk people.
Yeah, so they, I mean, they want to reduce their risk, and so they send a lot of complicated questions to kind of go through. So we highly recommend getting a cyber insurance policy. Um, and then, uh, security. The next one is email backup, right? So, um, the majority of people are using either Microsoft 365 or G Suite for email, contacts, calendars, you know, files. You know, a lot of people use Google Drive or OneDrive or SharePoint, and you know, those services do have protection gaps such as human error, recycle bin limitations, and different service limitations. So we recommend finding a third-party, you know, solution to back up all of your data. So it's, it's really more than just email backup, but your contacts, email, calendars, files, and and so forth. And then last and final security layer we recommend is a team-based password vault, so password management tool, and a process documentation tool. That last, that second half is really more of a bonus. But you've got to get, you know, if you're keeping passwords in a Word file or Excel or a note in your contact card on your phone, you know, the odds are many of you listening to this— oh, oh man, that's me. Uh, yeah, I know it happens. It's still popular. Uh, you've got to get a password management tool like 1Password, Dashlane, LastPass, right? There's a lot of solutions, but a password management tool is going to help you create unique passwords for each of your logins so that if and when Netflix is breached or, you know, a different site is breached, that's a unique password. It's not one that you're reusing a whole bunch different sites. So it also helps you kind of manage it team-wise, right? So let's say you've got an employee that leaves. What happens to all the accounts that they had created? Where are those passwords? Do you have control over that, right? So, you know, at the end of the day, to kind of wrap it up here, a layered approach to your firm security with these protections in place are going to go a long way in reducing your risk, right? But having a shopping list is not the same as having a meal. So the next steps, what you want to do, and if you've downloaded the worksheet that I provided, it has all these 8 security layers. You know, the next steps for you to identify the specific solutions you're going to use for each security layer, right? Maybe you can pick, you know, 1 or 2 or 3 at a time and say, hey, how can I, you know, roll out 1 or 2 of these each month, right, for the next 6 months or something like that? You know, so you've got to find out what you're going to— what service are you going to use, sign up for the accounts, complete the initial setup and configuration, learn how to use the solutions, enroll and teach them to your team, and work with an insurance agent to get a cyber insurance policy and complete the security questionnaire as well. Now, if all those steps overwhelm you again and you're like, oh man, don't— you told us about the time issue, Tom, how are we supposed to do all this? So again, knowing what to do is not going to stop you from getting hacked. Act. Um, I had, I, I had a lawyer I spoke with about 7 weeks ago. We went over, you know, we talked about her practice. She was based out of New York, but she works in California. Very successful solo, I think like $50K monthly revenues or something like that. And she's like, hey, I want to address my security. And we had a long talk about her concerns, and, and she never signed up, even though she gave me the impression she was going to. 2 weeks ago, I got a frazzled email from her saying, Tom, I've been hacked. You know, they got into my Chase, my banking, and all these different things. And so we had a call last week, and she's like, Tom, I've spent 30 to 40 hours just in the past week. And I heard from her on Monday, she's still dealing with it and putting more time into it. And I was like, man, what about all your client appointments? She's like, yeah, I've had to reschedule and delay work and miss deadlines and things like that. So, you know, the sad truth is most solos never get this addressed because they lack, you know, the awareness, right? Do you understand the threat? They lack the time. How can I take care of this? They lack the clarity. What do I need, and it's hard to implement, right? Who's going to do it? So again, that's why we've built BobaGuard, and it's, it's really a turnkey offering that's made all of these solutions accessible, you know, to solo and small firm lawyers. And we've got a 66-minute process to kind of get everything up and running, so it takes very little time. Um, so if you want to find out more, we've got our security checklist for busy lawyers at bobaGuard.com/checklist-nc. And I want to open it up for questions. Anything I might be able to help with that I didn't cover, or anything that I shared that was really confusing, or anything I can help with at all. I'm here to stay as long as you will stay, and as long as I can provide value and answer questions. So you can unmute yourself if you have a question, or you can, you know, type it in into the chat.
Thanks, Tom. And while you were talking, I glanced at my phone and I saw a message from Facebook from Walt Mossberg, who is the New York Times tech reporter and columnist and then started Recode and all this other stuff. Anyway, he put a picture of his wife on his Facebook account. And he says, my wife, Edie Mossberg, appears to have been hacked here. She saw a strange post in her name, so she set up a new account with a new photo. See this new photo below. She needs to rebuild her friend list, so if you get a friend request from her new account and you were already her friend on the old account, please accept it. I don't even know if this is real, you know. I mean, this is— that's the— what's the crazy thing about all of this? It's so hard to tell what is real and what is fake, um, because I'm not personal friends with Walt Mossberg. I mean, I'd love to be, but this is his like public persona on Facebook, and he's got a picture of his wife, and that she's been hacked and all this stuff. And it's just, you know, the landscape is so complex and so scary and so ever-changing. Hannah says she feels like MFA is low-hanging fruit. Are there other easy things like that we can do? Tom, I'm sure you feel the same way. I think I literally took my sister and my husband's phone. I asked them both, I said, do y'all have two-factor setup? Two-factor authentication or multi-factor authentication is where you can use either your device, like your phone, to get text messages as a secondary factor before you can log in with a username and password, or you can set up something like Google Authenticator, Microsoft Authenticator if you don't trust, and there's reasons not to trust your text messages as the second factor, But that kind of thing, actually, we're using Keeper at the bar for password management, which includes the, the two-factor authentication as part of the product and some of the other password managers out there. But if you turn on two-factor and you get a password manager and you make sure that all of your passwords are different for each login, which you can do just as you're logging into stuff, go and change your password. I use LastPass. Pass Premium, which means I also get dark web monitoring, so it'll tell me if the password's been exposed. There's— I think those two things alone, um, are just extremely necessary. But with the MFA, like I said, I took my husband's phone and my sister's phone and I turned on two-factor on, you know, their 6 or 7 primary accounts, and it took me about 15 minutes minutes per, per device. So it's not hard to do, it's just taking the time to do it. I also get a lot from attorneys, well, if I turn on MFA, do I have to do it every single time? No, because you can tell it to remember devices. So you can have it remember your password or your, your laptop, or you can have it remember your phone. But there are some, um, there's some sites that I don't have it remember the, the factor, or that remember the device. So for instance, my bank account, I have to go through two-factor every single time, or my credit cards accounts, things like that, because I, I don't ever want to get too comfortable with that.
Yeah, no, I agree. I think, you know, MFA or 2FA is one of the easiest low-hanging fruit, and then using a password manager, you know, I think breaking that habit of using the 3 passwords you've always had And, you know, the, the risk— what happened to me, I'll tell you a personal story. I had been using— I use one— my team and I use 1Password, and I had used it for many years, but I still had old passwords from my lazy days, right? And when we set up the dark web scanning, we had actually no hits under globemacit.com, under that domain, but then I put in my personal email address, my my wife's, my chief of operations, every single one of us had multiple hits. And a lot of them, I was like, oh, whoa, that's one of the ones I, you know, I used to reuse. So I had to go out and change like 27 passwords that night. It was not fun and it was, you know, tedious, but I slept better. You know, so using a password manager, using unique passwords, you know, I think if there's two strategies that you did, it's enable two-factor authentication authentication, you know, make a list. What are all the websites that would cause you a lot of heartache if they got hacked, right? So, you know, QuickBooks, case management, file management, email, um, you know, make that list and then just check each one, right? Two-factor authentication while you're in there, change your password, make it unique, make it long and complex. You know, that's the benefit of using a password manager also is it generates a password for you where if you're not using that feature you're coming up with your own passwords, you're using your kids' names, your dog's names, your birth date, you know, you're merging all those together and they're predictable. And a lot of that information is available and can be found on the web. You know, all those cool little Facebook polls, "Oh hey, who is your favorite cartoon character from the '90s?" You know, and everyone's like, "Oh, Spider-Man," you know, whatever it was, right? And that's all data that's being kind of sourced. Now, I don't want to put on my tin hat too much, but you think of security questions and things like that. There are polls that collect, essentially people are volunteering information like the street you grew up on when you were 6, right? 10, 15, 20 years ago, no one would've ever been able to figure that out. Now it's not that hard. Hard to do, right? So yeah, unique passwords, password through a password manager, and 2FA, I would say, are the easiest ones.
Yep. And, and we could probably— and we, we could definitely talk about this all day because it— well, while Tom was talking, it occurred to me, things like knowing how to remotely wipe your phone if you accidentally lose your phone. You think, I won't lose my phone. I left my phone in the back of a cab, um, and I had to remotely wipe it after I, you know, I did as much as I could to try to get it back and then had to give up. So you turn your phone into a disposable device. It's a very expensive disposable device, but you back up everything and then you know how to remotely wipe it. And there's, you know, there's little things that you can do to keep yourself safe. If someone asks you for your password, never, ever, ever, nobody, not in your firm, not outside of your firm, Don't ever share your password. There's no reason that they should have it. So, you know, I guess I hate that I looked at the Walt Mossberg thing and immediately questioned its reliability and, you know, authentic authenticity. But that's kind of the world we live in. And if you're in real estate practice, you know already that you're, you're pretty high-level targets because a lot of money is transferring through your hands. And, you know, you probably get as many risk alerts and fraud alerts from your cyber liability and your insurance company to keep, keep aware of that. But it's not just that. I had a, I had a friend who's in a law firm who said that their, their Exchange server that was on-premise was hacked through the, the recent Exchange hack., and cost them a whole lot of money.
So, um, this is stuff that happens. One thing we didn't talk about that's, that's really important to be aware of also is the, the level of sophistication, right, in cyber criminals. These are not, you know, computer geeks living in their mother's basement eating Cheetos and like, oh, I'm going to see if I can hack into this. This. It's like, no, it is, you know, organized crime. They've, you know, they run Monday morning team meetings, they do daily huddles, they have quarterly goals, they wear a suit and tie to work, they get dressed up, they've got great budgets, and they don't have to play by the rules like most other business owners, you know. And, and they're smart, they study psychology, they know that your willpower is considerably lower at 4 PM on a Friday than Monday morning at 10:00 AM, you think about marketing, right? Oh, what are the best days to hold webinars? What's the best day to send a webinar invite to get the most schedules, right? They do the same thing, but for the work that they're doing, hey, which days and times get the highest phishing open rates, right? So they're studying that, they're aware of it. How can we, they read, you know, pre-suasion and the psych— you know, the Robert Cialdini books, right, on influence and things like that. And so they're aware of all these concepts as well. And, you know, that's how— you know, you know Neil, right, Neil Tyra. That's how he fell for it. He got an email from his friend. He knew the email address. Email signature was exactly the same. You know, a couple weeks ago, one of our clients sent us a phishing email that they suspected, and it was a complete replica of their website. It was actually hosted on spark.adobe.com, so it wasn't like, you know, some crazy weird URL, right? And it was a mirror copy of their home page, which, you know, a responsive modern web page and all that. I mean, it's— and, and so they know the factors that, hey, if we see we put our guard down because we, you know, the social proof and different things. And so they're using all these different, you know, marketing tactics and social proof and different things to increase their open rates, right? Their phishing success rates and all that stuff.
So yeah. Okay, well, I don't see any other questions. Tom, do you have a slide that has your contact information?
No, but that would be smart. I'll put it in.
I will share it with everybody in case you want to get in touch with Tom directly and ask him any other questions. It's in the chat as well. It's tom@bobegard.com. And with that, again, email Tom, email me. I'll stop the recording. I will put this up online. I'll get Tom's materials. I'll send them out to you. And thanks for participating today. Next month we are going to shift gears quite dramatically and talk about project management tools and using one that you probably already have through Microsoft 365 and the Planner product. So stay tuned.
Thanks, everybody.