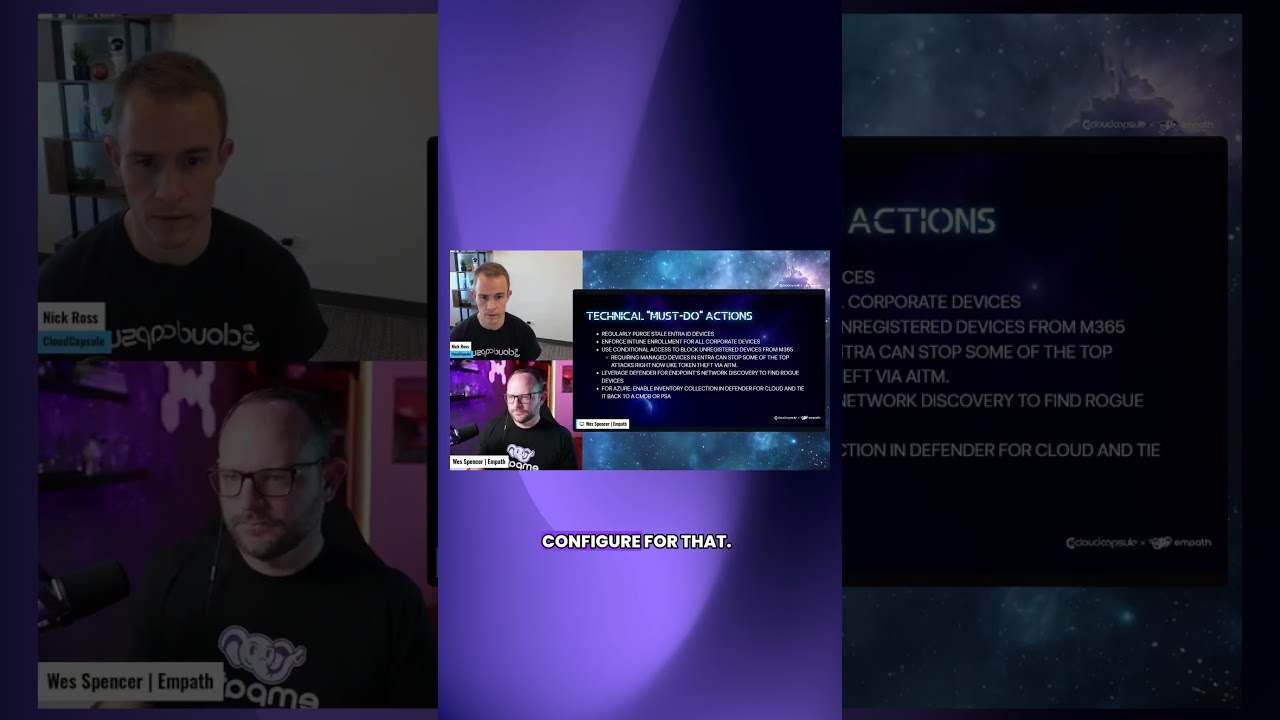
MSPs can enforce zero-trust by requiring only managed devices access corporate data. Use Microsoft Intune and clear SOPs to prevent random device registration, then layer on compliance checks over time to tighten security.
Chapters
How does a device gain trust, right, to the network, as an example of that? Or if you're zero trust, right, it's how does it gain access to data and how do you trust that to perform that process? So there's definite, you know, SOPs we've typically had in places before, but it's basically saying, how can anyone such as a regular user not go in and just register a device, right? We have restrictions that we can put into place that aren't there by default. There's some settings in Microsoft that you can configure for that, but also starting to think about leveraging tools like Intune, as an example, to get them fully under management and get them to a higher level of "compliance" in that sense, right? The first step is just getting and saying, "Hey, we have managed devices. Everybody else that's not on a managed device can't access corporate data, 101," right? That's what you should strive to do in every client environment. The next step up is saying, "We want to have stricter policy checks for what we're looking for." that says that this device isn't going, you know, enough or getting outside of compliance as well too.